

Researchers have uncovered an active campaign exploiting a zero-day vulnerability in the Zimbra email platform.
Zimbra is an email platform available under an open source license. According to the developer, the platform supports hundreds of millions of mailboxes located in 140 countries.
On February 3, cybersecurity researchers from Volexity, Steven Adair and Thomas Lancaster, said the system is being exploited by a threat group tracked as TEMP_Heretic in a series of spear phishing email attacks.
In a security advisory, Volexity said the campaign, dubbed “Operation EmailThief,” was first discovered in December 2021 and is likely the work of Chinese cybercriminals.
According to the team, TEMP_Heretic is careful in its selection of potential victims. The threat actor will first perform reconnaissance and will use tracker-embedded emails to see if an address was valid and if a target would even open emails in the first place — and if so, the second stage of the attack chain triggers.
In total, 74 unique Microsoft Outlook email addresses have been used to send the preliminary emails, which contain generic images and subjects including invitations, alerts, and airline ticket refunds.
TEMP_Heretic will then send tailored phishing emails containing a malicious link. The more targeted themes of subsequent emails related to interview requests from news organizations, including the AFP and BBC, as well as invitations to charity dinners. Other phishing email samples collected were more generic and contained holiday greetings.
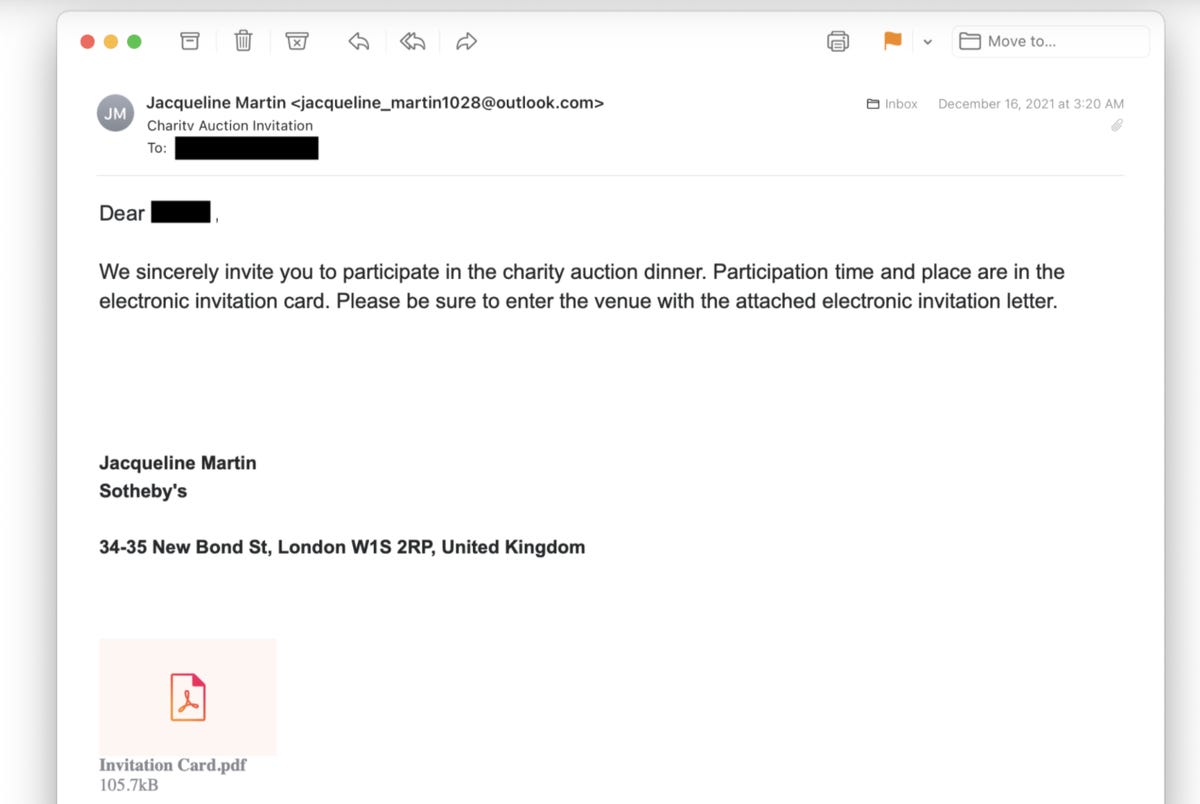
Volexity
The victim would need to be logged into the Zimbra webmail client from a web browser when they opened the malicious attachment & link for the exploit to be successful — but according to Volexity, the link itself could be launched from other apps, such as Outlook or Thunderbird.
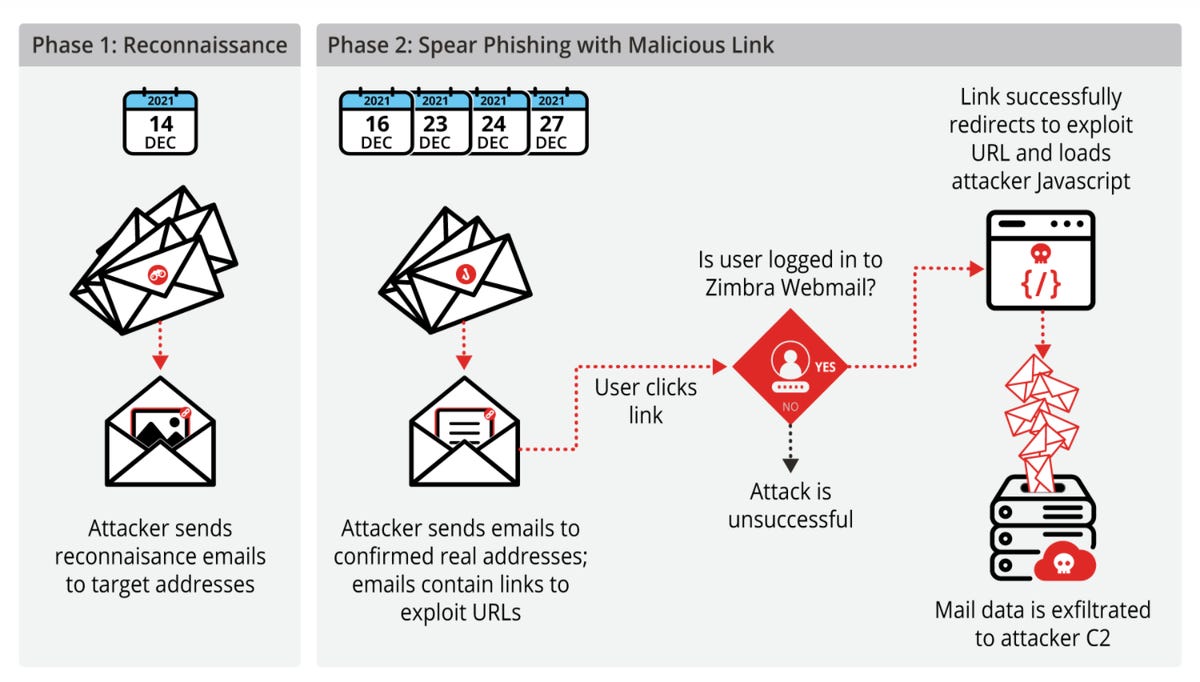
Volexity
The cross-site scripting (XSS) vulnerability allows attackers to run arbitrary JavaScript in the context of the Zimbra session, leading to the theft of mail data, attachments, and cookies. In addition, cybercriminals could leverage a compromised email account to send further phishing emails or to launch prompts for the victim to download additional malware payloads.
TEMP_HERETIC has previously been linked to campaigns targeting European government and media organizations.
“At the time of writing, this exploit has no available patch, nor has it been assigned a CVE (i.e., this is a zero-day vulnerability),” the researchers say. “Volexity can confirm and has tested that the most recent versions of Zimbra — 8.8.15 P29 & P30 — remain vulnerable; testing of version 9.0.0 indicates it is likely unaffected.”
Volexity notified Zimbra of the exploit attempt on December 16 and provided proof-of-concept (PoC) code. Zimbra acknowledged the report on December 28 and confirmed to the cybersecurity team that the exploit was valid.
After requesting details of a patch in January, but having received no response, Volexity then made its findings public this month. However, users who have upgraded to the latest version of the webmail client are unlikely to be at risk.
“Users of Zimbra should consider upgrading to version 9.0.0, as there is currently no secure version of 8.8.15,” the researchers say.
ZDNet has reached out to Zimbra and we will update when we hear back.
Previous and related coverage
Have a tip? Get in touch securely via WhatsApp | Signal at +447713 025 499, or over at Keybase: charlie0

